Single sign-on lets your team sign in to View My Desktop with the work account they already use for email and everything else. It's one less password for them, and one less thing for you to clean up when someone leaves: turn off their work account, and their remote access goes with it.
View My Desktop uses SAML 2.0, which every major identity provider supports. This guide covers Okta, Microsoft Entra ID, and Google Workspace, and the same steps work for others.
What you need
- A View My Desktop team on the Team plan, and to be its owner. Admins can verify domains and switch single sign-on on or off, but only the owner can connect the identity provider in step 3.
- An admin account at your identity provider, to add a new app there.
- Access to your domain's DNS, to prove the domain is yours.
Everything is on the Team page, under Single sign-on, in four numbered steps.
1. Verify your email domain
Type the domain your team's email addresses use, like example.com, and choose Add domain. View My Desktop shows a TXT record to add at your DNS provider. Add it there, wait a few minutes, and choose Verify.
This proves your business owns the domain. A verified domain belongs to one team only.
2. Add View My Desktop to your identity provider
Step 2 on the Single sign-on tab lists three details: the Entity ID, the Reply URL (ACS), and a Metadata link. Make a new SAML app at your provider with those, and have it send each person's work email as the NameID.
Okta
- In the Okta Admin Console, open Applications, then Create App Integration, and choose SAML 2.0.
- Name it View My Desktop.
- Set Single sign-on URL to the Reply URL, and Audience URI (SP Entity ID) to the Entity ID.
- Set Name ID format to EmailAddress and Application username to Email.
- Finish, assign the people or groups who should use it, and download the app's SAML metadata from its Sign On tab.
Microsoft Entra ID
- In the Microsoft Entra admin center, open Enterprise applications and choose New application, then Create your own application.
- Name it View My Desktop and choose the option for an application you don't find in the gallery.
- Under Single sign-on, choose SAML.
- In Basic SAML Configuration, set Identifier (Entity ID) to the Entity ID and Reply URL to the Reply URL.
- Under Attributes & Claims, make sure the Unique User Identifier (Name ID) is the person's email address.
- Download the Federation Metadata XML, and assign users or groups under Users and groups.
Google Workspace
- In the Google Admin console, open Apps, then Web and mobile apps, choose Add app, then Add custom SAML app.
- Name it View My Desktop and continue.
- Download the IdP metadata on the next screen.
- Set ACS URL to the Reply URL and Entity ID to the Entity ID. Set Name ID format to EMAIL and Name ID to Primary email.
- Finish, then turn the app on for everyone or for the groups who should use it.
3. Connect your identity provider
Back on the Single sign-on tab, paste the metadata XML your provider gave you into step 3 and choose Save. If your provider doesn't offer a metadata file, choose No metadata file? Type the details instead and enter its entity ID, sign-in URL, and signing certificate.
4. Turn it on
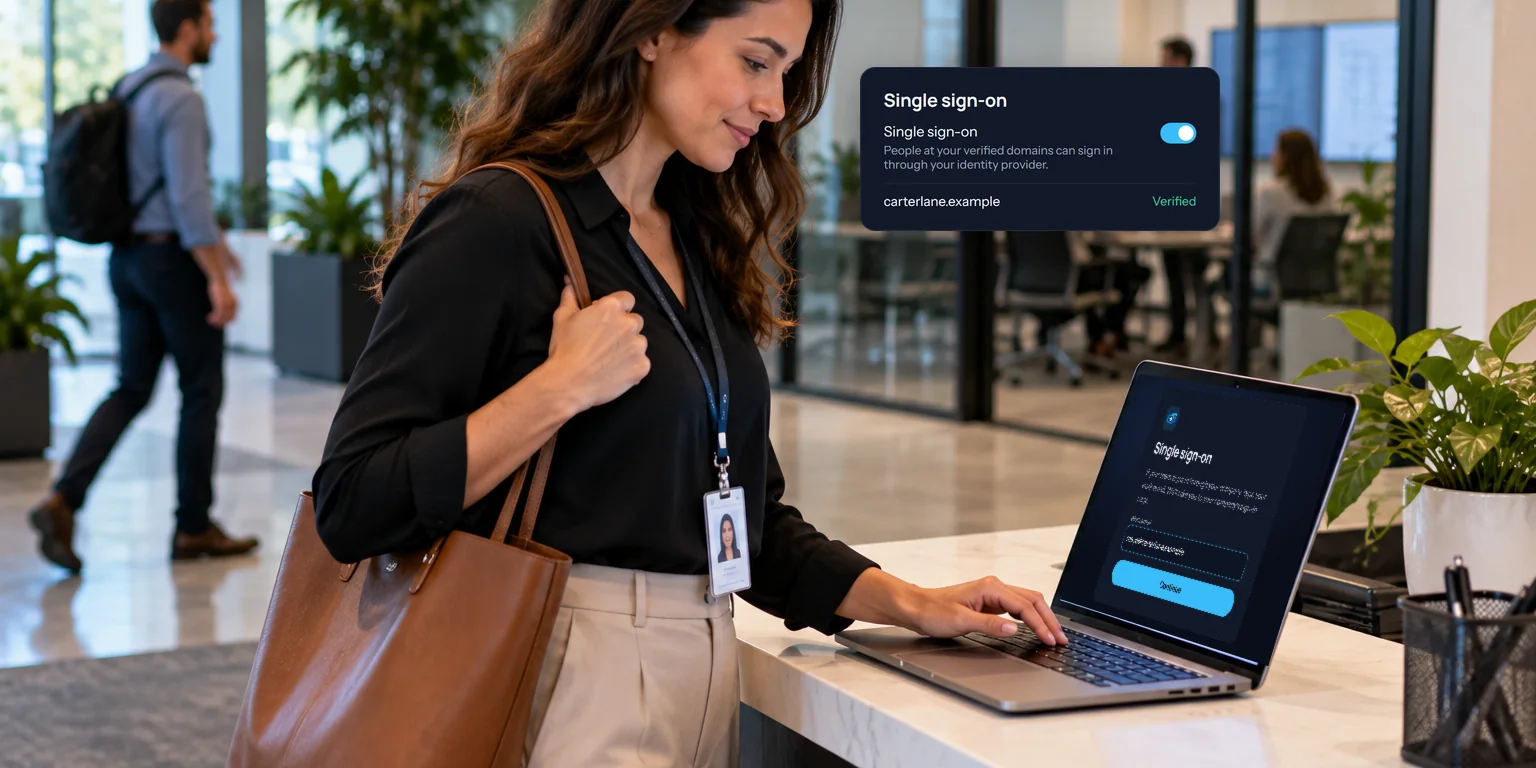
Switch on Single sign-on and save. People at your verified domains can now sign in through your provider.
To make it the only way in, also switch on Require it. Members at your verified domains then have to sign in through your provider from their next sign-in. The team's owner can still use a password, so the team is never locked out if the provider has a bad day.
How your team signs in
On the View My Desktop sign-in page, they choose Use your company's single sign-on, type their work email, and choose Continue. They're taken to your provider's sign-in page, then straight back in.
Things to know
- People must already be on the team. Single sign-on signs in existing members. It doesn't add new people, so invite them first, using their work email.
- Start from View My Desktop. Signing in from your provider's app dashboard won't work. For security, each sign-in has to start on our sign-in page.
- Certificates run out. The tab shows when your provider's signing certificate expires. When the provider moves to a new one, paste its new metadata in step 3.
- The website first. For now, single sign-on works on the website, and the phone app doesn't offer it yet. If you require it, members at your verified domains use the website until the app catches up.
Questions people ask
Does it work with other providers?
Yes, with any provider that supports SAML 2.0, such as OneLogin, JumpCloud, or Ping. The details in step 2 are the same.
What happens when someone leaves the company?
Once their work account is turned off at your provider, they can't sign in. Remove them from the team as well, as our small team guide describes.